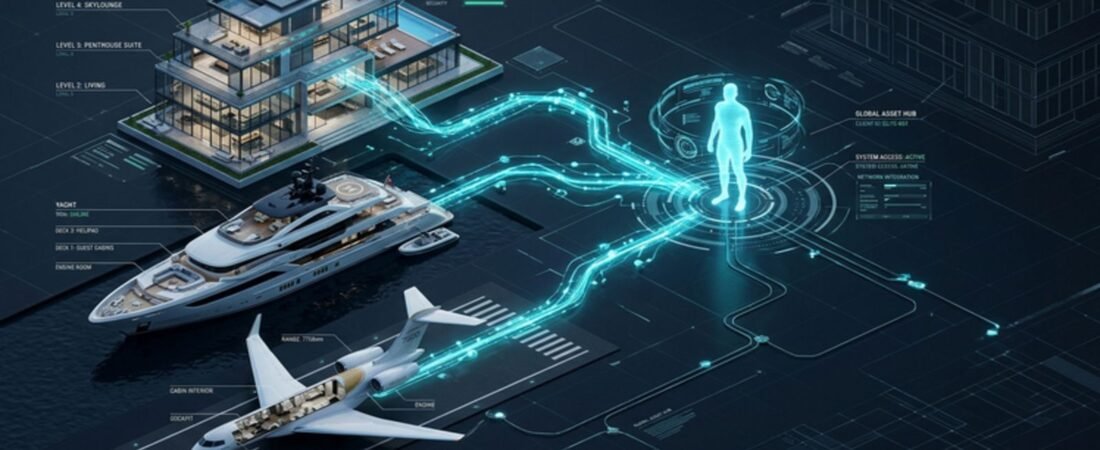
The digital estate of a billionaire in 2026 no longer resembles a fortress with walls and a moat.It is a borderless attack surface where a Principal’s personal Gmail, a yacht’s navigation system, and a smart home’s HVAC controller are all entry points of equal value to a determined attacker. The 2026 threat landscape has fundamentally shifted: billionaires are no longer hunted for credit card data or retail identity theft. They are targeted for institutional access — the ability to impersonate decision-makers, manipulate transactions, and extort across generational wealth structures.
State-sponsored actors, organized synthetic fraud syndicates, and AI-augmented social engineers now target not just liquid capital but the long-term integrity of family data, reputation, and succession planning. The family office must be audited not as a corporate entity, but as a multi-generational digital estate requiring full information control — an operating posture that assumes every device, every conversation, and every encrypted file is already under passive surveillance.
This audit examines the three most serious threat categories that have matured in 2026: real-time deepfake synthesis used to authorise fraudulent wire transfers; luxury IoT ecosystems serving as pivot points into core financial infrastructure; and Store Now, Decrypt Later (SNDL) campaigns that could render today’s encryption worthless that render today’s encryption tomorrow’s plaintext. Each threat demands a forensic defense strategy that moves beyond conventional endpoint detection and response (EDR) into quantum-resistant cryptography, physical verification protocols, and the merger of physical and digital security. This audit is written for the Family Office CIO, private wealth counsel, and the executive protection director who now shares equal responsibility for the Principal’s digital security.
Cyber Audit: The UHNW Digital Perimeter
Audit Finding: The traditional network perimeter is extinct. For billionaire digital estates, the attack surface now encompasses biometric data, synthetic media, quantum-vulnerable legacy encryption, and IoT telemetry from superyachts to smart penthouses. Full information control means treating the Principal as the infrastructure — any breach of their personal devices is a breach of the office.
Control Objective: Implement zero-trust architecture: verify every request explicitly, authenticate through physical channels, and assume breach across all data layers.
The “Shadow Executive” Threat: Auditing AI-Synthesized Deepfakes in Family Office Operations
Business Email Compromise (BEC) has changed fundamentally in 2026. What began as crude spoofed email domains has evolved into synthetic identity fraud where attackers deploy real-time AI voice cloning and video deepfakes to impersonate Principals, CFOs, and family members with near-perfect fidelity. The January 2024 Arup deepfake incident—in which a finance employee authorized 15 wire transfers totaling $25.6 million after a video call with a synthetic CFO and synthetic colleagues—served as the prototype for what is now an industrial-scale threat. As of early 2025, none of the $25.6 million had been recovered — and the case remains unsolved.
In 2026, generative AI models require as little as three seconds of audio sample to produce a convincing voice clone, and real-time face-swap algorithms can operate within browser-based video conferencing platforms without specialized hardware. The FBI IC3 reported that AI-powered BEC drove $2.77 billion in losses across 21,442 incidents in 2024, with deepfake-augmented fraud becoming operationally scalable as threat actors moved from proof-of-concept to industrial deployment. Human detection accuracy for high-quality deepfake video has fallen to approximately 24.5% (Korshunov & Marcel), well below the 50% a coin flip would produce — rendering visual verification protocols unreliable for critical authorisations.
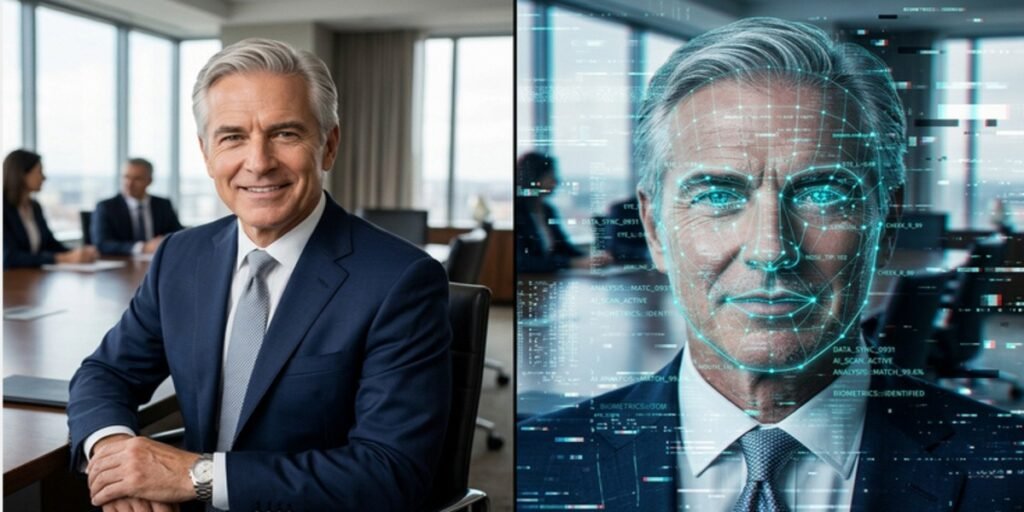
For the family office, the attack chain has shifted from phishing for credentials to synthesising trusted identities. Attackers no longer need to breach the email server; they need only harvest public conference footage, earnings calls, or social media clips to create a convincing synthetic double. UHNW deepfake protection 2026 requires more than employee training; it demands a fundamental restructuring of authorization architecture. Family offices must abandon video and voice as standalone verification vectors for high-value transactions.
The forensic defense strategy centers on Out-of-Band (OOB) Analog Verification—a protocol where any transaction exceeding material thresholds (typically £1M or equivalent) requires a physical, non-digital confirmation mechanism. This includes pre-arranged duress codes, callback verification through independently sourced contact numbers, and in-person countersignatures. Voice biometric anomaly detection and behavioral analytics can serve as supplementary controls, but they cannot be the primary gate. The family office must also conduct regular synthetic identity exposure audits—mapping the Principal’s digital footprint to identify publicly available audio and video assets that could be harvested for cloning, then systematically reducing that surface through privacy-focused takedown services and legal entity anonymization.
The Invisible Breach: Hardening the IoT Ecosystem of Luxury Smart Estates
The modern luxury smart estate is a network of networks—HVAC controllers, biometric access systems, private cinema automation, marina dock sensors, and satellite communications—all converging on a central management plane that often shares logical proximity with the family office’s financial servers. This convergence gives attackers a clear path from peripheral systems into core infrastructure. While the Colonial Pipeline attack demonstrated the vulnerability of critical infrastructure, the 2026 audit reveals that a breach of a Principal’s personal Gmail or the estate’s unpatched IoT gateway can cascade directly into the family office’s core financial systems.
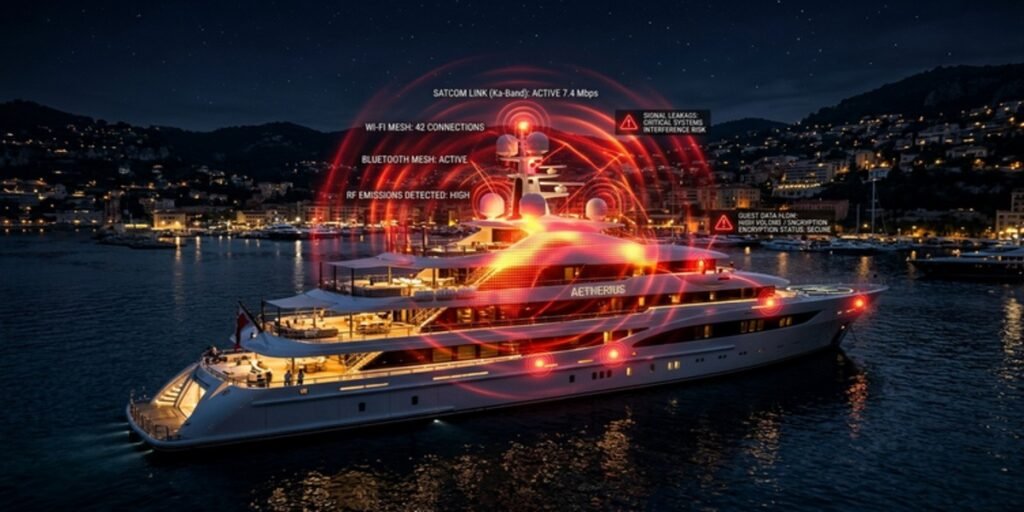
Superyachts and private jets represent particularly acute attack surfaces. The private marine sector lacks the cybersecurity standards imposed on commercial shipping, leaving owners to self-regulate in an environment where third-party vendors—navigation software providers, entertainment system integrators, and telemetry maintenance firms—routinely introduce vulnerabilities that can cascade across the vessel’s entire network. Vulnerabilities in onboard navigation systems, satellite communications, and guest Wi-Fi networks can allow adversaries to intercept data, jam GPS positioning, and pivot into connected personal devices. Once inside the guest network, adversaries can execute lateral movement into operational technology (OT) systems or, via the Principal’s synced devices, into the family office’s core data repositories.
Luxury home automation security in 2026 requires strict network segmentation. The family office must insist on complete isolation between estate IoT devices and financial infrastructure. This is not merely a VLAN configuration; it requires air-gapped servers where the core ledger, succession documents, and cryptographic key material reside on physically isolated networks with no internet connectivity and unidirectional data flow. Smart estate devices should operate on dedicated, monitored subnets with zero trust enforcement at every hop. Biometric access logs, surveillance footage, and environmental controls must be treated as sensitive data in their own right—not convenience features—requiring encryption at rest and strict access governance. For the family office managing multiple residences across jurisdictions, each property must be audited as a separate security domain with no implicit trust between estates.
Quantifying the “Reputation Tax”: The Forensic Cost of Data Exfiltration
Data encryption is no longer sufficient. The 2026 threat landscape is defined by Store Now, Decrypt Later (SNDL)—a strategy in which state-sponsored actors and advanced persistent threats (APTs) passively harvest encrypted data today with the explicit intention of decrypting it once quantum computing reaches cryptanalytic relevance. This is not theoretical. The NSA publicly confirmed in 2021 that adversaries were actively collecting encrypted data for future exploitation, and the UK’s NCSC reiterated in 2023 that state actors conduct data theft campaigns “for exploitation in years to come.” In early 2025, Google executives Kent Walker and Hartmut Neven published a policy brief warning that SNDL attacks are already underway, with adversaries harvesting encrypted financial records, trade secrets, and classified communications at scale for future quantum decryption.
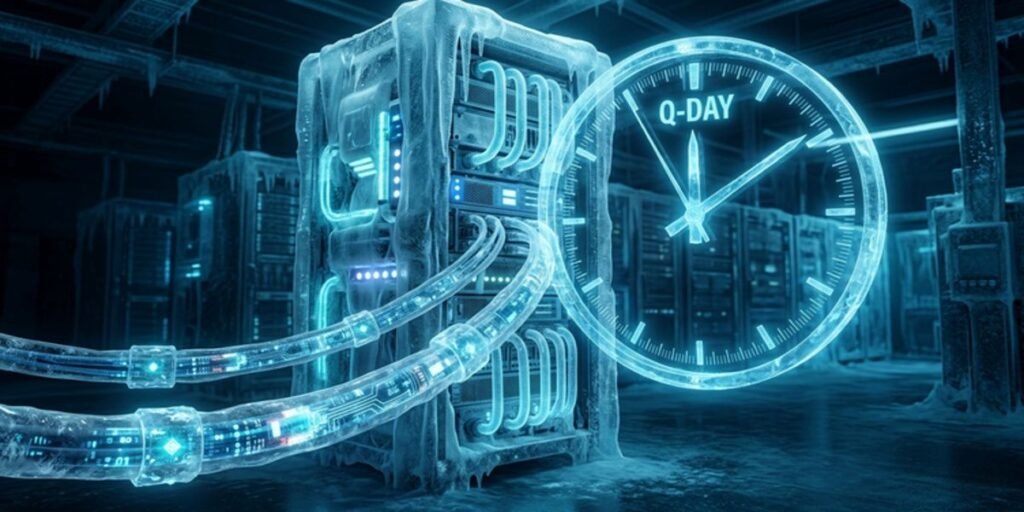
The exposure timeline is straightforward. Data encrypted today with RSA or ECC algorithms—still the standard across most family office infrastructures—will be vulnerable to Shor’s algorithm once a cryptographically relevant quantum computer (CRQC) is operational, with credible estimates placing Q-Day between 2033 and 2040. Estimates vary — some agencies cite 2030–2035 for constrained scenarios — meaning any single timeline is unreliable and the conservative approach is to assume the shortest window. For dynastic wealth with 20- to 50-year confidentiality horizons—trust documents, genetic data, offshore structuring, political affiliations—data exfiltrated in 2026 will remain valuable and decryptable long after the current Principal has passed. The Mosca Inequality formalises this risk: if x + y > z — where x is the time needed to migrate, y is the number of years the data must stay confidential, and z is the years until a CRQC is operational — then the data is already compromised in principle.
Post-quantum encryption for private wealth is therefore not an IT upgrade — it is a fiduciary obligation. In August 2024, NIST finalized its first post-quantum cryptographic standards: ML-KEM (FIPS 203) for key encapsulation and ML-DSA (FIPS 204) for digital signatures, with SLH-DSA (FIPS 205), formerly SPHINCS+, as a hash-based digital signature backup. Google has migrated key exchanges for all internal traffic and Google Cloud-native services to ML-KEM by default, removing the feasibility argument and establishing a baseline expectation for institutional-grade data protection.
Family offices must immediately begin cryptographic discovery—mapping every instance of RSA, ECDH, and ECDSA across their estate—and prioritize hybrid deployments that layer post-quantum algorithms alongside classical cryptography during transition. Symmetric encryption (AES-256) and hashing (SHA-3) remain quantum-resistant and do not require replacement, but every public-key exchange protecting long-lived data must be transitioned by 2027 to meet emerging CNSA 2.0 and EU Cyber Resilience Act mandates. The EU Cyber Resilience Act entered into force in December 2024 and becomes fully applicable from December 2027, requiring all products with digital elements sold in the EU — including wealth management platforms — to meet baseline cybersecurity requirements throughout their lifecycle.
The UHNW privacy valuation extends beyond direct financial loss. Data exfiltration triggers compounding costs: forensic investigation, legal exposure across jurisdictions, regulatory scrutiny, and permanent damage to the Principal’s privacy. For families where reputation is itself a balance-sheet asset, the true cost of a breach often far exceeds the direct monetary loss.
2026 Threat Vector Benchmark
Practical Protocols: Physical Verification, Cyber-Physical Security, and Succession Planning
The “Protocol of Silence”: Out-of-Band Authentication and the Analog Duress Code
The 2026 shift toward Out-of-Band (OOB) Authentication represents a deliberate regression from digital convenience to analog certainty. For any transaction exceeding £1 million, the digital signature—whether cryptographic token, biometric scan, or MFA push—is no longer considered sufficient. The Zero-Trust Dynasty model mandates a physical, non-digital verification layer: a pre-arranged analog duress code exchanged through a trusted courier, a voice-verified callback to a landline with a known, static number, or an in-person countersignature by a designated Family Council member.
The duress code is particularly critical; it is a word or phrase that, when inserted into any verification conversation, silently signals to the recipient that the Principal is under coercion without alerting the attacker. This protocol acknowledges a harsh reality: if an adversary can synthesize the Principal’s face and voice in real time, only physical-world knowledge shared outside the digital domain can authenticate intent.
Cyber-Physical Convergence: The Executive Protection Agent as Cyber-First Responder
In 2026, the distinction between physical security and cybersecurity has dissolved. Executive Protection (EP) agents are now trained as cyber-first responders whose primary responsibility includes managing the Principal’s signal emissions—the constant broadcast of RF, Bluetooth, Wi-Fi, NFC, and cellular metadata that creates a trackable digital exhaust. An EP detail in 2026 does not merely clear rooms for listening devices; it conducts RF spectrum analysis to detect anomalous base stations, manages Faraday-shielded transport for devices, and enforces “digital clean zones” where the Principal’s hardened phone is the only active transmitter.
The bodyguard’s job now includes acting as a physical firewall—ensuring that the Principal’s personal devices never connect to untrusted networks, that Bluetooth remains disabled in all public spaces, and that the physical proximity of the Principal to their devices is treated as a cryptographic control. This convergence recognizes that a zero-click exploit like Pegasus or Predator requires no user interaction; the only defense is preventing the exploit’s delivery vector from ever reaching the device.
The ‘Digital Will’ Protocol: Cyber-Succession Planning and ICE Vaults
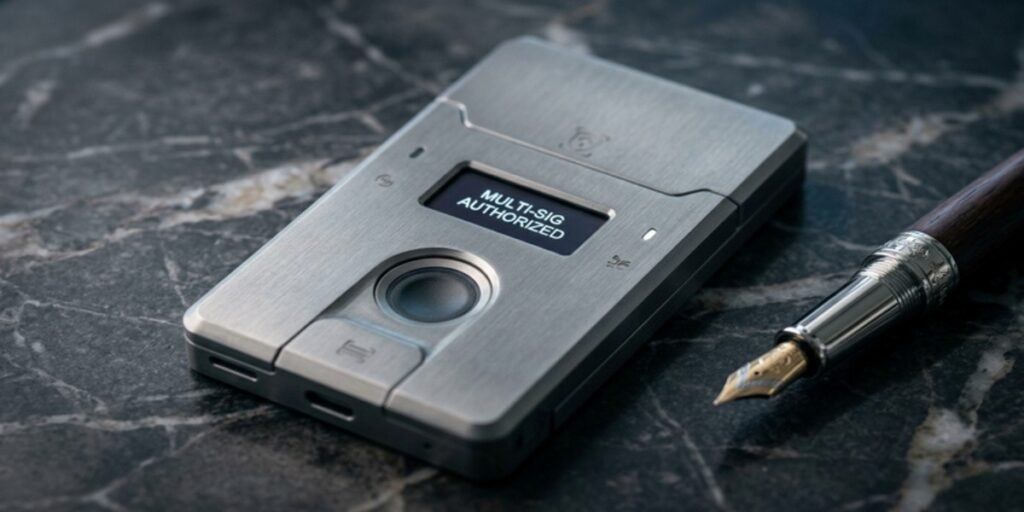
Most family office collapses are not caused by market volatility but by key-person dependency—the catastrophic scenario in which only the Principal possesses the master cryptographic keys, seed phrases, or access credentials to critical digital assets. The 2026 audit introduces the Cyber-Succession Plan: a formally structured, legally governed protocol for encrypted “In Case of Emergency” (ICE) digital vaults. These vaults contain the complete inventory of the family’s digital estate—cryptocurrency keys, offshore account credentials, encrypted correspondence, digital asset NFTs, and cloud infrastructure admin access—stored under multi-signature or threshold cryptographic schemes that require multiple trustees to reconstruct.
Unlike traditional password managers, ICE vaults for UHNW estates employ time-locked smart contracts or dead man’s switch protocols that activate only upon verified incapacitation or death, preventing premature access while ensuring continuity. The vault itself should be distributed across geographically separated, air-gapped hardware security modules (HSMs) with no single point of failure. Every family office must audit its succession plan annually, updating credentials and verifying that heirs and trustees possess the technical literacy to execute the protocol without compromising its security.
Frequently Asked Questions
Q. What is the most secure phone for a billionaire in 2026?
There is no single “most secure” device; security is a function of attack surface reduction and operational discipline. In 2026, the recommended architecture for UHNW Principals is a hardened, minimalist device running a privacy-focused operating system with verified boot, no pre-installed bloatware, and a strictly controlled app environment. Devices like the Purism Librem 5 or similarly hardened handsets with hardware kill switches for microphone, camera, Bluetooth, and cellular modem provide physical layer control. However, the device itself is secondary to the operational protocol: the phone must never connect to public Wi-Fi, must operate on a dedicated MVNO with strict SIM control, must use only Signal or similar encrypted messaging with disappearing messages enabled, and must be replaced on a 12-month cycle to mitigate zero-day accumulation. For maximum sensitivity, the Principal should maintain a secondary “clean” device used exclusively for a single purpose—e.g., one device for family office banking, never used for browsing, social media, or travel.
Q. How do you prevent deepfake wire fraud?
Prevention requires defense in depth across three layers. First, technical controls: deploy real-time deepfake detection on all video conferencing platforms, with audio and video analyzed simultaneously for synthetic artifacts; implement behavioral analytics that flag anomalous linguistic patterns or urgency cues. Second, process controls: enforce dual-authorization for all wire transfers above a defined threshold; mandate OOB verification through a pre-established analog channel; implement a “cooling-off” period of 24 hours for non-recurring payees. Third, human controls: conduct quarterly adversarial simulations using synthetic media to test employee resilience; establish a “no shame” reporting culture where staff are incentivized to verify rather than comply. The Arup case demonstrated that even sophisticated finance professionals can be deceived by high-fidelity synthetic video; the only reliable defense is a protocol that assumes all digital identity claims are fraudulent until proven otherwise through an independent channel.
Q. Does a VPN protect a family office from Pegasus-class spyware?
No. A VPN encrypts traffic in transit but provides zero protection against zero-click exploits that target the device itself. Pegasus, Predator, and comparable mercenary spyware operate by exploiting vulnerabilities in the phone’s operating system—typically through iMessage, FaceTime, or browser rendering engines—requiring no user interaction and no network-level interception. Once installed, the spyware operates with kernel-level privileges, bypassing VPN encryption entirely by capturing data before it reaches the tunnel. Protection against Pegasus-class threats requires: (1) hardened OS with rapid patch deployment; (2) minimalist app environments that eliminate the attack surface (no email, no social media, no browsing on the sensitive device); (3) network isolation where the device never connects to untrusted infrastructure; (4) regular forensic imaging to detect anomalies; and (5) threat intelligence monitoring for indicators of compromise associated with mercenary spyware campaigns. A VPN is a privacy tool for untrusted networks; it is not a counter-surveillance tool against nation-state or mercenary-grade endpoint compromise.
The core lesson of 2026 is that the Individual is now the Infrastructure. A breach of a Principal’s personal Gmail is a breach of the family office’s entire liquidity position. The convergence of personal and institutional attack surfaces means that protecting the billionaire requires the same institutional-grade rigor as protecting a sovereign nation’s critical infrastructure — because, for the adversary, the two are now indistinguishable.
Regulatory Disclosure & Institutional Disclaimer
Informational Purpose Only: This cybersecurity audit is provided by Elites Mindset for educational and illustrative purposes regarding 2026 threat landscapes. It does not constitute cybersecurity, legal, or technical advice. The mention of specific tools, platforms, or protocols does not imply formal endorsement or a commercial partnership unless explicitly stated.
Accuracy: While Vasid Qureshi and our editorial team strive for accuracy in threat intelligence and technical references, readers are advised that the cybersecurity landscape is subject to rapid change.
Independent Due Diligence: Family Office Principals and CIOs should engage qualified cybersecurity professionals and legal counsel before implementing changes to their security architecture. Elites Mindset assumes no liability for security incidents resulting from the application of frameworks discussed herein.
© 2026 Elites Mindset. All Rights Reserved.